Security
Four more fixes for your VPS this week
A backdoored OVHcloud CLI, a Brotli bug in Node.js, a BIND flaw that mostly affects Kerberos setups and a CVSS 10 in GitLab, and what each means for a small server.
Security
A backdoored OVHcloud CLI, a Brotli bug in Node.js, a BIND flaw that mostly affects Kerberos setups and a CVSS 10 in GitLab, and what each means for a small server.
Privacy
A leaked flyer claims Cellebrite can unlock iPhone 11 to 16 from eight metres away. It is not a mass remote exploit, and it isn't confirmed. If your phone could be taken from you, it still changes what you should do.
Security
Two critical PHP flaws let an unauthenticated request run code on a PHP server before your application's login page loads. Patched releases are out, and anything you run on PHP, from billing front ends to phpMyAdmin, needs them now.
Security
Eight eMudhra intermediate CA keys were small enough to guess. Browsers blocked them within hours and Chrome drops the root on 27 October. Curl, old Go builds and stale trust stores are where the risk now sits.
Security
A header-compression flaw lets one connection exhaust an HTTP/3 server's memory. Hysteria2, Xray and sing-box all inherit it through quic-go, and many builds that look patched are not.
Investigations
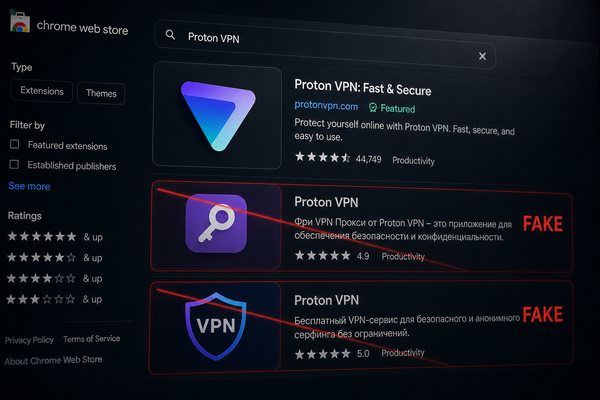
Kush Pandya found 274 Chrome extensions wearing other people's VPN brands. They set a SOCKS5 hop on port 1082 for a shop called Myxa.
Investigations
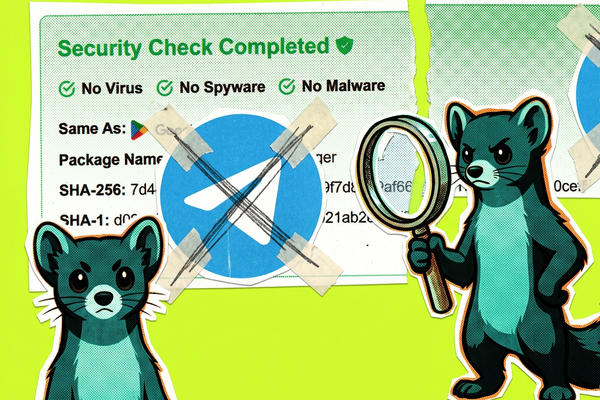
A repackaged Telegram APK on APKPure contained a collector that exfiltrated messages, media and contacts to a server previously running a simple Collector Dashboard.
Investigations
Your WireGuard public key can tie your sessions together across Mullvad servers. That's exactly the sort of subtle linkage that privacy-conscious users assume does not exist.
zero-day
A single week saw Linux, Windows, macOS, Next.js, and the global software supply chain battered by critical exploits and mass advisories. Is this the long-feared AI-driven collapse of digital infrastructure, or just the new normal? A technical, evidence-driven investigation.
supply-chain
ℹ️This is a developing situation I have relied on JDownloader for years. It is the sort of unglamorous tool you install once and forget about until you need to pull a 40 GB archive at 3 a.m. So when the official site went dark on 7 May and

Linux
A subtle 2017 optimisation in the Linux kernel's crypto layer has just been turned into a reliable, 732-byte path from any user account to root. Here's what it means for your servers and what to do right now.
supply-chain
A stolen Roblox auto-farm script led to Context.ai credentials, then Vercel Google Workspace takeover via OAuth token abuse in March 2026.